A hot potato: Despite recent controversies over its corporate policies, Synology still holds a large slice of the increasingly popular NAS market. When its devices are hit by dangerous security flaws, customers should take note. Hackers and cyber-criminals certainly will.
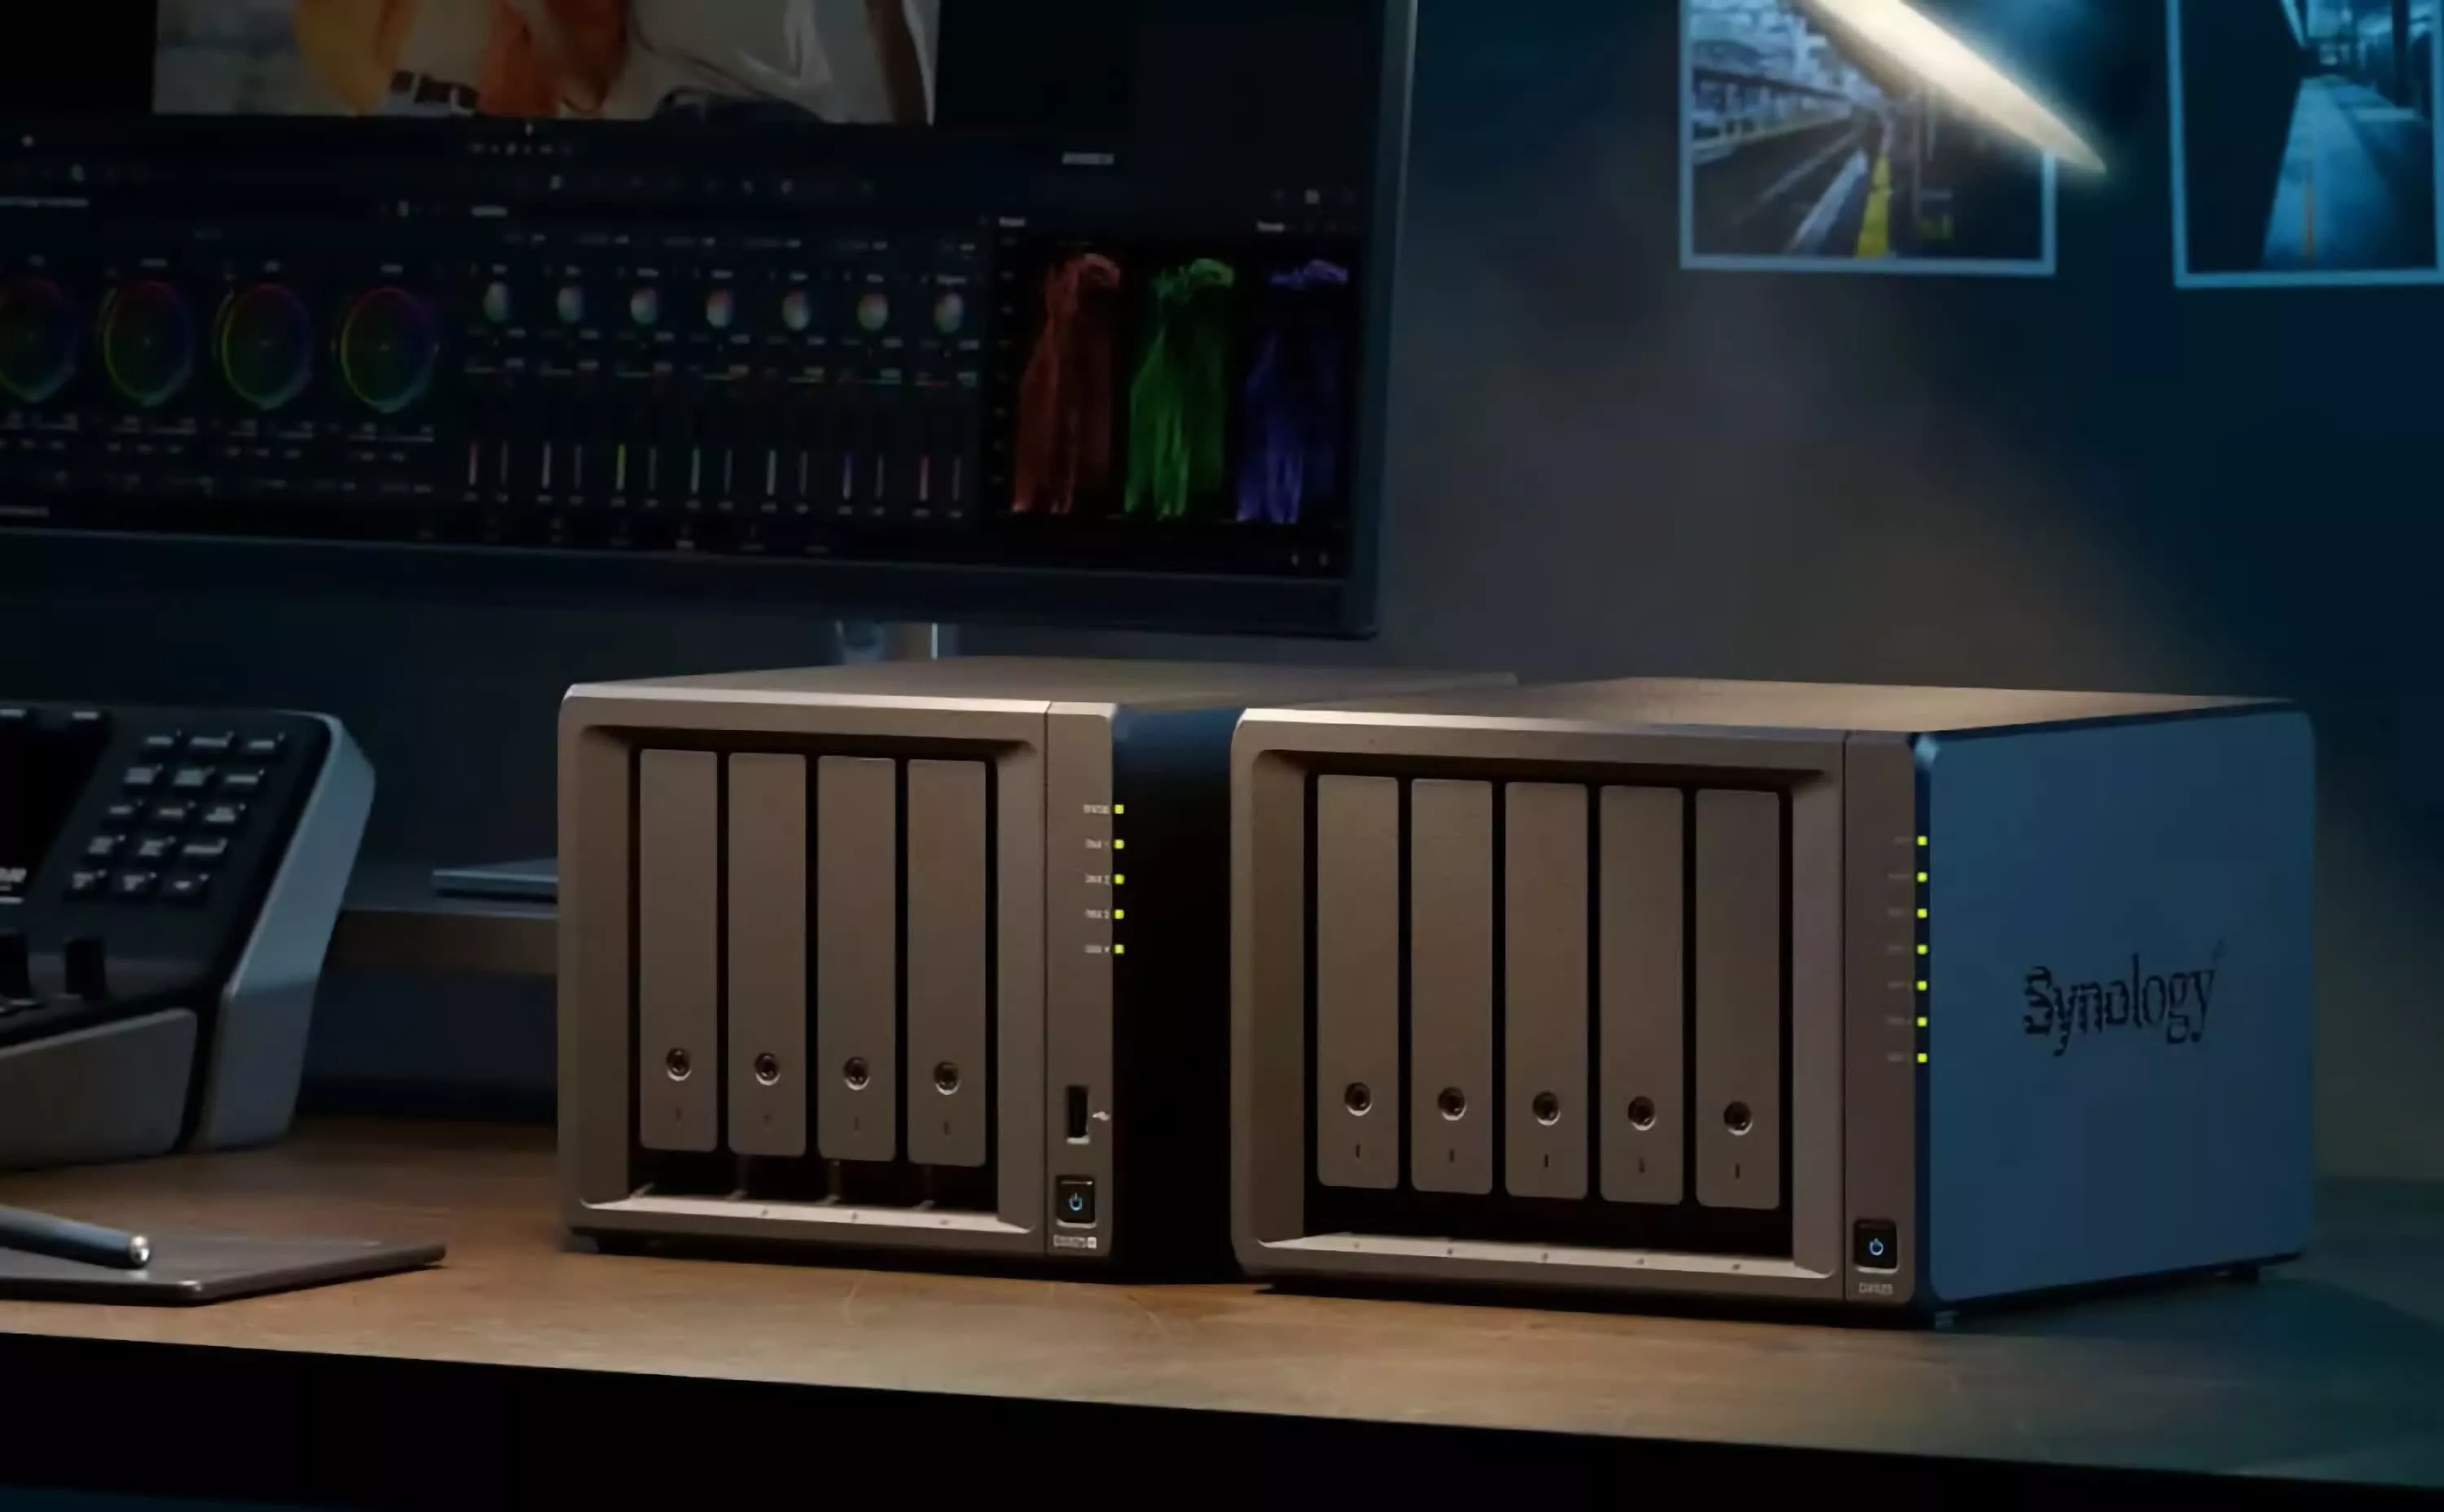
A newly published security advisory discloses two serious vulnerabilities in DiskStation Manager (DSM), the Linux-based OS used in Synology NAS products, one of them rated critical. The storage maker warned that the flaws could be abused to remotely access and attack vulnerable devices, giving cyber-criminals – or rogue AI agents, for that matter – an easy avenue to wreak havoc on users' data and local IT infrastructure.
Synology rates the SQL injection flaw "critical," with a 9.8 out of 10 score – the flaw could be abused to remotely access and attack vulnerable devices.
The advisory focuses on two vulnerabilities, tracked as CVE-2026-76954 and CVE-2026-85101. The first is an SQL injection bug in DSM's Auth API that lets remote attackers read or write arbitrary files, or carry out denial-of-service (DoS) attacks.
The second was found in DSM's rsync tool and could let attackers bypass authentication entirely to read specific files, write arbitrary files, or launch "limited" DoS attacks.
Synology rates the SQL injection flaw "critical," with a 9.8 out of 10 score in the Common Vulnerability Scoring System (CVSS). The rsync bug is classed as "important," with an 8.6 base CVSS score. Both can be exploited remotely, without logging in, to attack vulnerable devices. Synology disclosed them roughly a month after releasing the DSM updates that fix them, a common practice that gives users time to patch before the details go public.
The NAS maker shipped the fixed DSM versions in October 2026, and the company now considers the issue "resolved." Users with automatic updates may already have the patch, but those on manual update policies should definitely check for new DSM releases. Fixes are available for DSM 7.4, 7.3, 7.2.2, and 7.2.1.
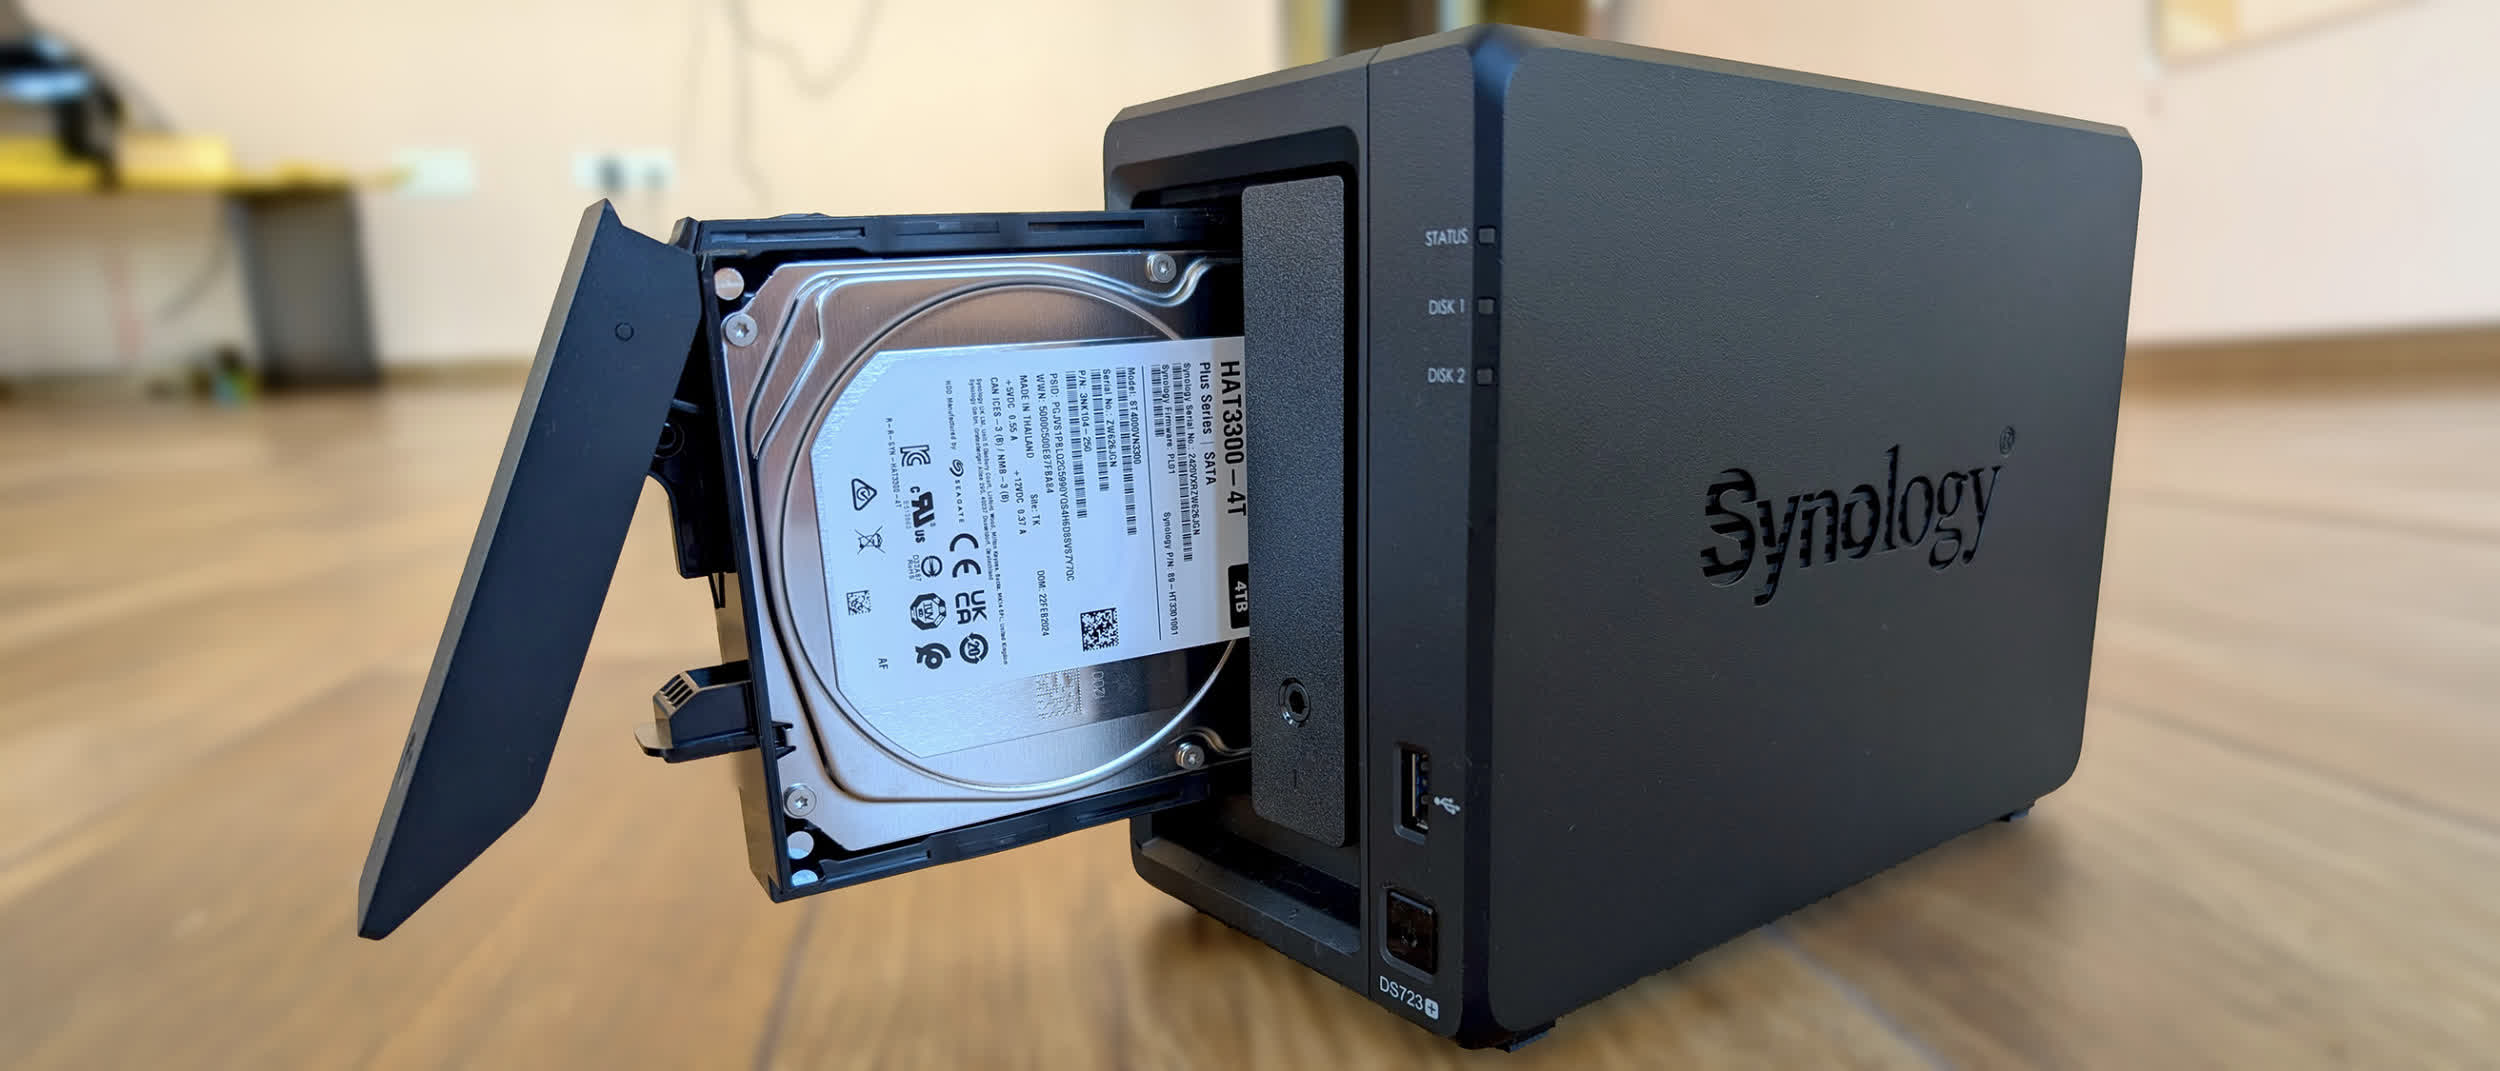
Synology credited external researchers from Viettel Cyber Security and Aytio with discovering and reporting the two flaws. Some users are calling the SQL injection bug in the login process an embarrassment for Synology's software stack, while others are touting their "satisfaction" at having replaced Synology's devices with competing NAS products.
The Taiwanese manufacturer was also criticized for forcing customers to use only "certified" hard disk drives in its NAS systems. The backlash grew so intense that Synology was ultimately forced to reverse course and let users install any HDD brand and model they wanted.
Synology patches a critical NAS flaw that could let attackers in without logging in


