
Why it matters: Chipmakers ship buggy code all the time, that alone isn't news. What makes WPSplinter stand out is that Broadcom apparently did issue a fix eight years ago, but that fix never reached the routers sitting in people's homes. Furthermore, the lack of a CVE kept the problem invisible to the advisories and patch pipelines that router makers and ISPs rely on.
Security researcher Quentin Kaiser detailed the flaw at the Hexacon conference in Paris on October 16. He calls it WPSplinter, a name he only gave it because Broadcom refused to issue an official identifier.
The bug sits in Broadcom's old code for WPS, the feature that lets you connect a device by pressing a button on the router instead of typing a password. That code mishandles how certain messages are exchanged and with the right sequence of them, it lets an attacker read the router's memory or run external code on the device.
The attacker doesn't need the Wi-Fi password or a completed WPS pairing. Being within radio range is enough. This also isn't the WPS PIN weakness that made headlines in the early 2010s. The problem is Broadcom's code, not WPS itself.
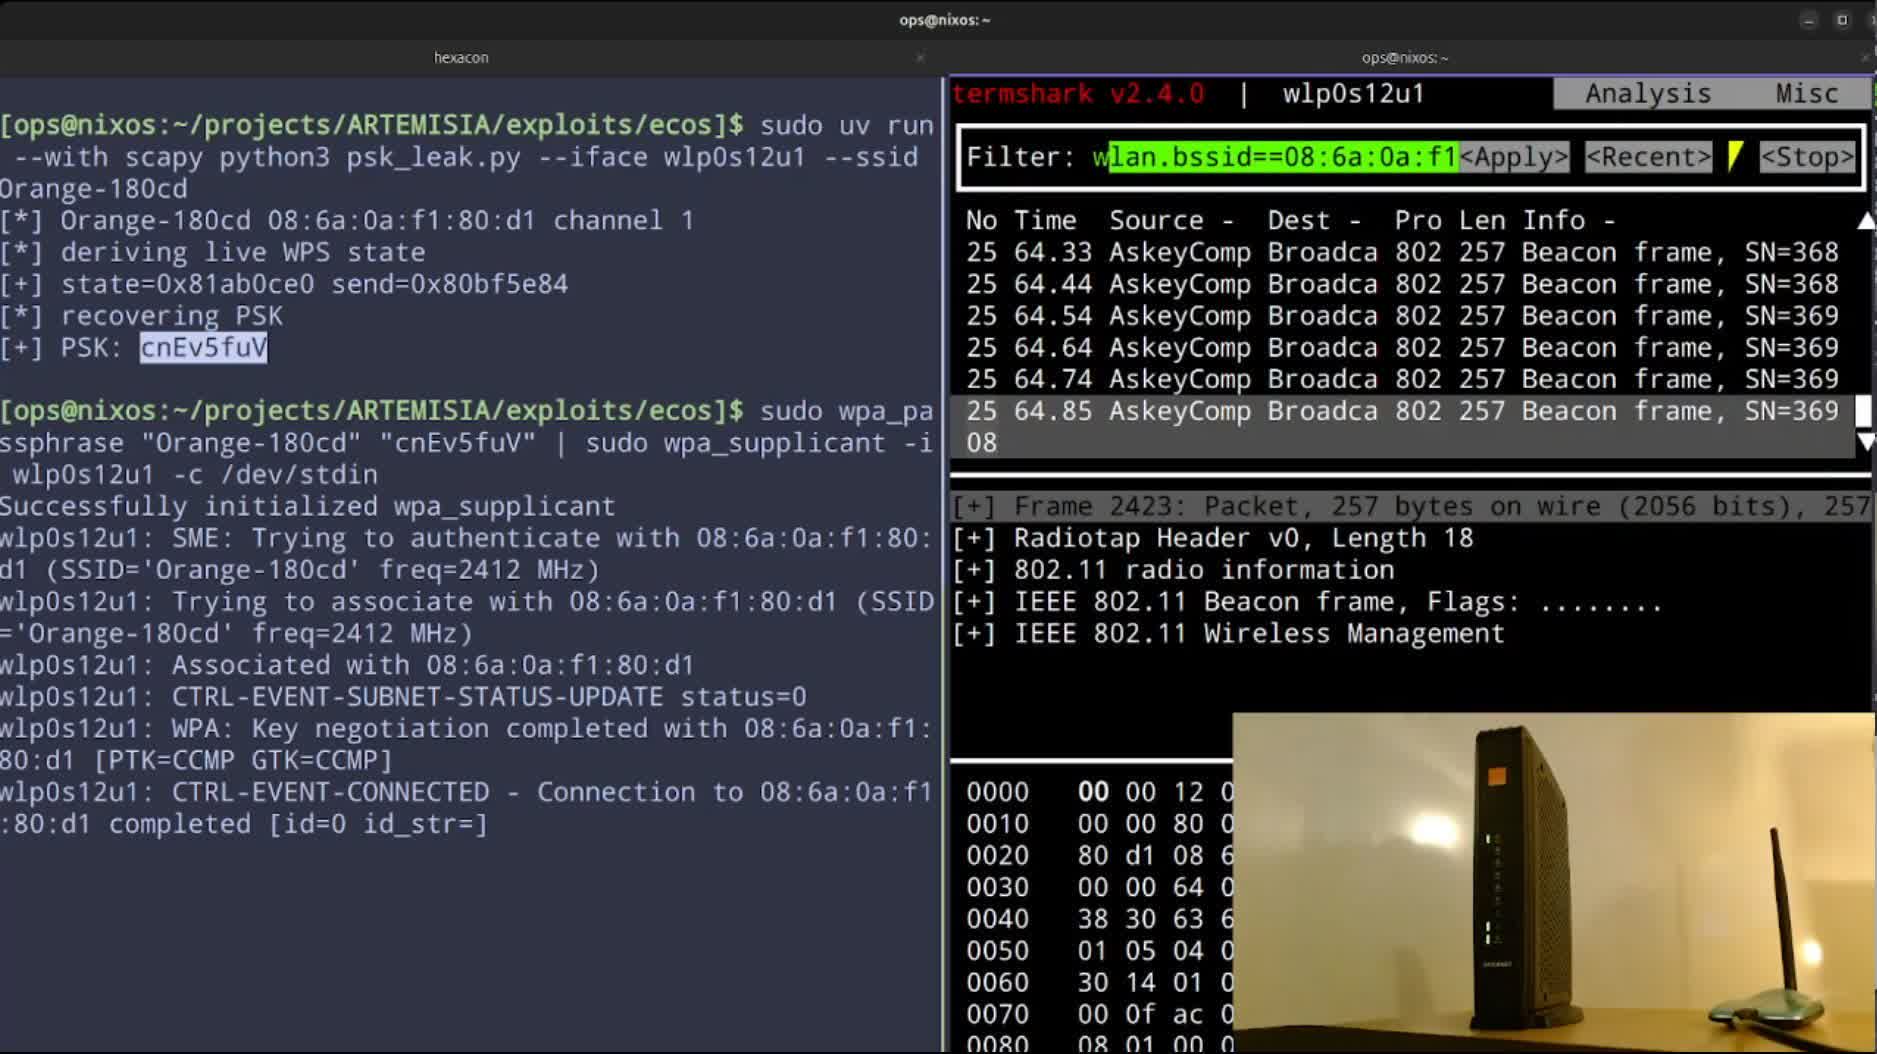
Kaiser's demos make the risk concrete. On an Askey TCG3000 gateway supplied by Orange Belgium, his exploit pulled the Wi-Fi key out of the device's NVRAM, sent it back over the air, and then used it to join the network. On a different device, a Proximus BBOX3V+ made by Sagemcom, he got a remote shell running entirely over Wi-Fi, with no internet connection needed on his end. He says the attack works over long distances.
One detail that won't surprise anyone at this point... Kaiser says AI helped him find the bug in less than a week, work that would have taken months by hand. Router firmware used to be protected partly by obscurity and by how tedious it was to dig through. That's no longer the case, for researchers or attackers.
Kaiser confirmed the bug on gateways from three of Belgium's four major ISPs: Proximus, Orange and VOO. By his count, that's about 1.5 million vulnerable devices in Belgium alone. But routers built on the same Broadcom chips are sold worldwide. His list of affected models, which he says is incomplete, includes gear from Cisco, TP-Link, Netgear, Sagemcom, Nokia, ZTE and Zyxel, deployed by ISPs like Movistar, Optus, KPN and Türk Telekom. That tally would put a closer global estimation in the low hundreds of millions.
When Kaiser reported the bug in July, Broadcom said it had known about it since 2018, had since replaced the old WPS code in its software, and that he should take it up with device makers. Kaiser says the 2018 patch to the old code was incomplete anyway. Broadcom also declined to request a CVE, calling the code obsolete and outside its support window.
On Hacker News, some argue that the blame is on router makers and ISPs for never updating. Kaiser's counterpoint is that without a CVE, the warning likely never made it down the supply chain.
Changing your Wi-Fi password won't help, since the attack happens before login. Turning off WPS is (always) worth doing, but Kaiser warns it may not fully disable the vulnerable code. If in doubt about your ISP's router firmware, it's best to switch off the gateway's Wi-Fi, put it in bridge mode, and use your own up-to-date router. Kaiser has also posted a detection script on GitHub for anyone who wants to check their hardware.
One last detail that won't surprise anyone at this point. Kaiser says AI tools helped him find the bug in under a week, work that would have taken months by hand. Router firmware used to be protected partly by obscurity and by how tedious it was to dig through. That's no longer the case, for researchers or attackers.