Wireshark is the world's leading network protocol analyzer, trusted by professionals across enterprises, governments, non-profits, and academia. It provides deep visibility into network activity, allowing users to inspect traffic at a granular level – essential for troubleshooting, analysis, development, and education.
Originally created by Gerald Combs in 1998, Wireshark has grown into a thriving open-source project powered by a global community of expert contributors and volunteers.
What should I look for when analyzing packets in Wireshark?
Wireshark is a powerful tool for troubleshooting specific network issues. Instead of scanning all traffic, focus on a particular problem, such as slow application performance or failed connections. Use filters to narrow down the data and look for anomalies like retransmissions, handshake failures, or unexpected protocol behaviors.
By applying filters based on IP addresses, protocols, or specific packet attributes, you can focus on the most relevant data for your analysis.
How do I filter traffic to a specific website in Wireshark?
To filter traffic for a specific website, first determine its IP address using the command nslookup [website] (e.g., nslookup www.techspot.com). Then, apply the filter ip.addr == [IP_ADDRESS] in Wireshark to isolate packets related to that site. For analyzing TCP connections, you can use filters like tcp.flags.syn == 1 && tcp.flags.ack == 0 to identify SYN packets
How can I capture traffic from specific devices on my network?
Capturing traffic from specific devices may require configuring your network appropriately. Use port mirroring on a managed switch or employ a network tap to direct the desired traffic to your monitoring system. Additionally, focusing on specific protocols, such as DNS, can provide insights into device activities.
Is Wireshark suitable for professional use in network analysis?
Yes. Wireshark is widely used in professional environments for network troubleshooting and analysis.
Features
- Deep inspection of hundreds of protocols, with more being added all the time
- Live capture and offline analysis
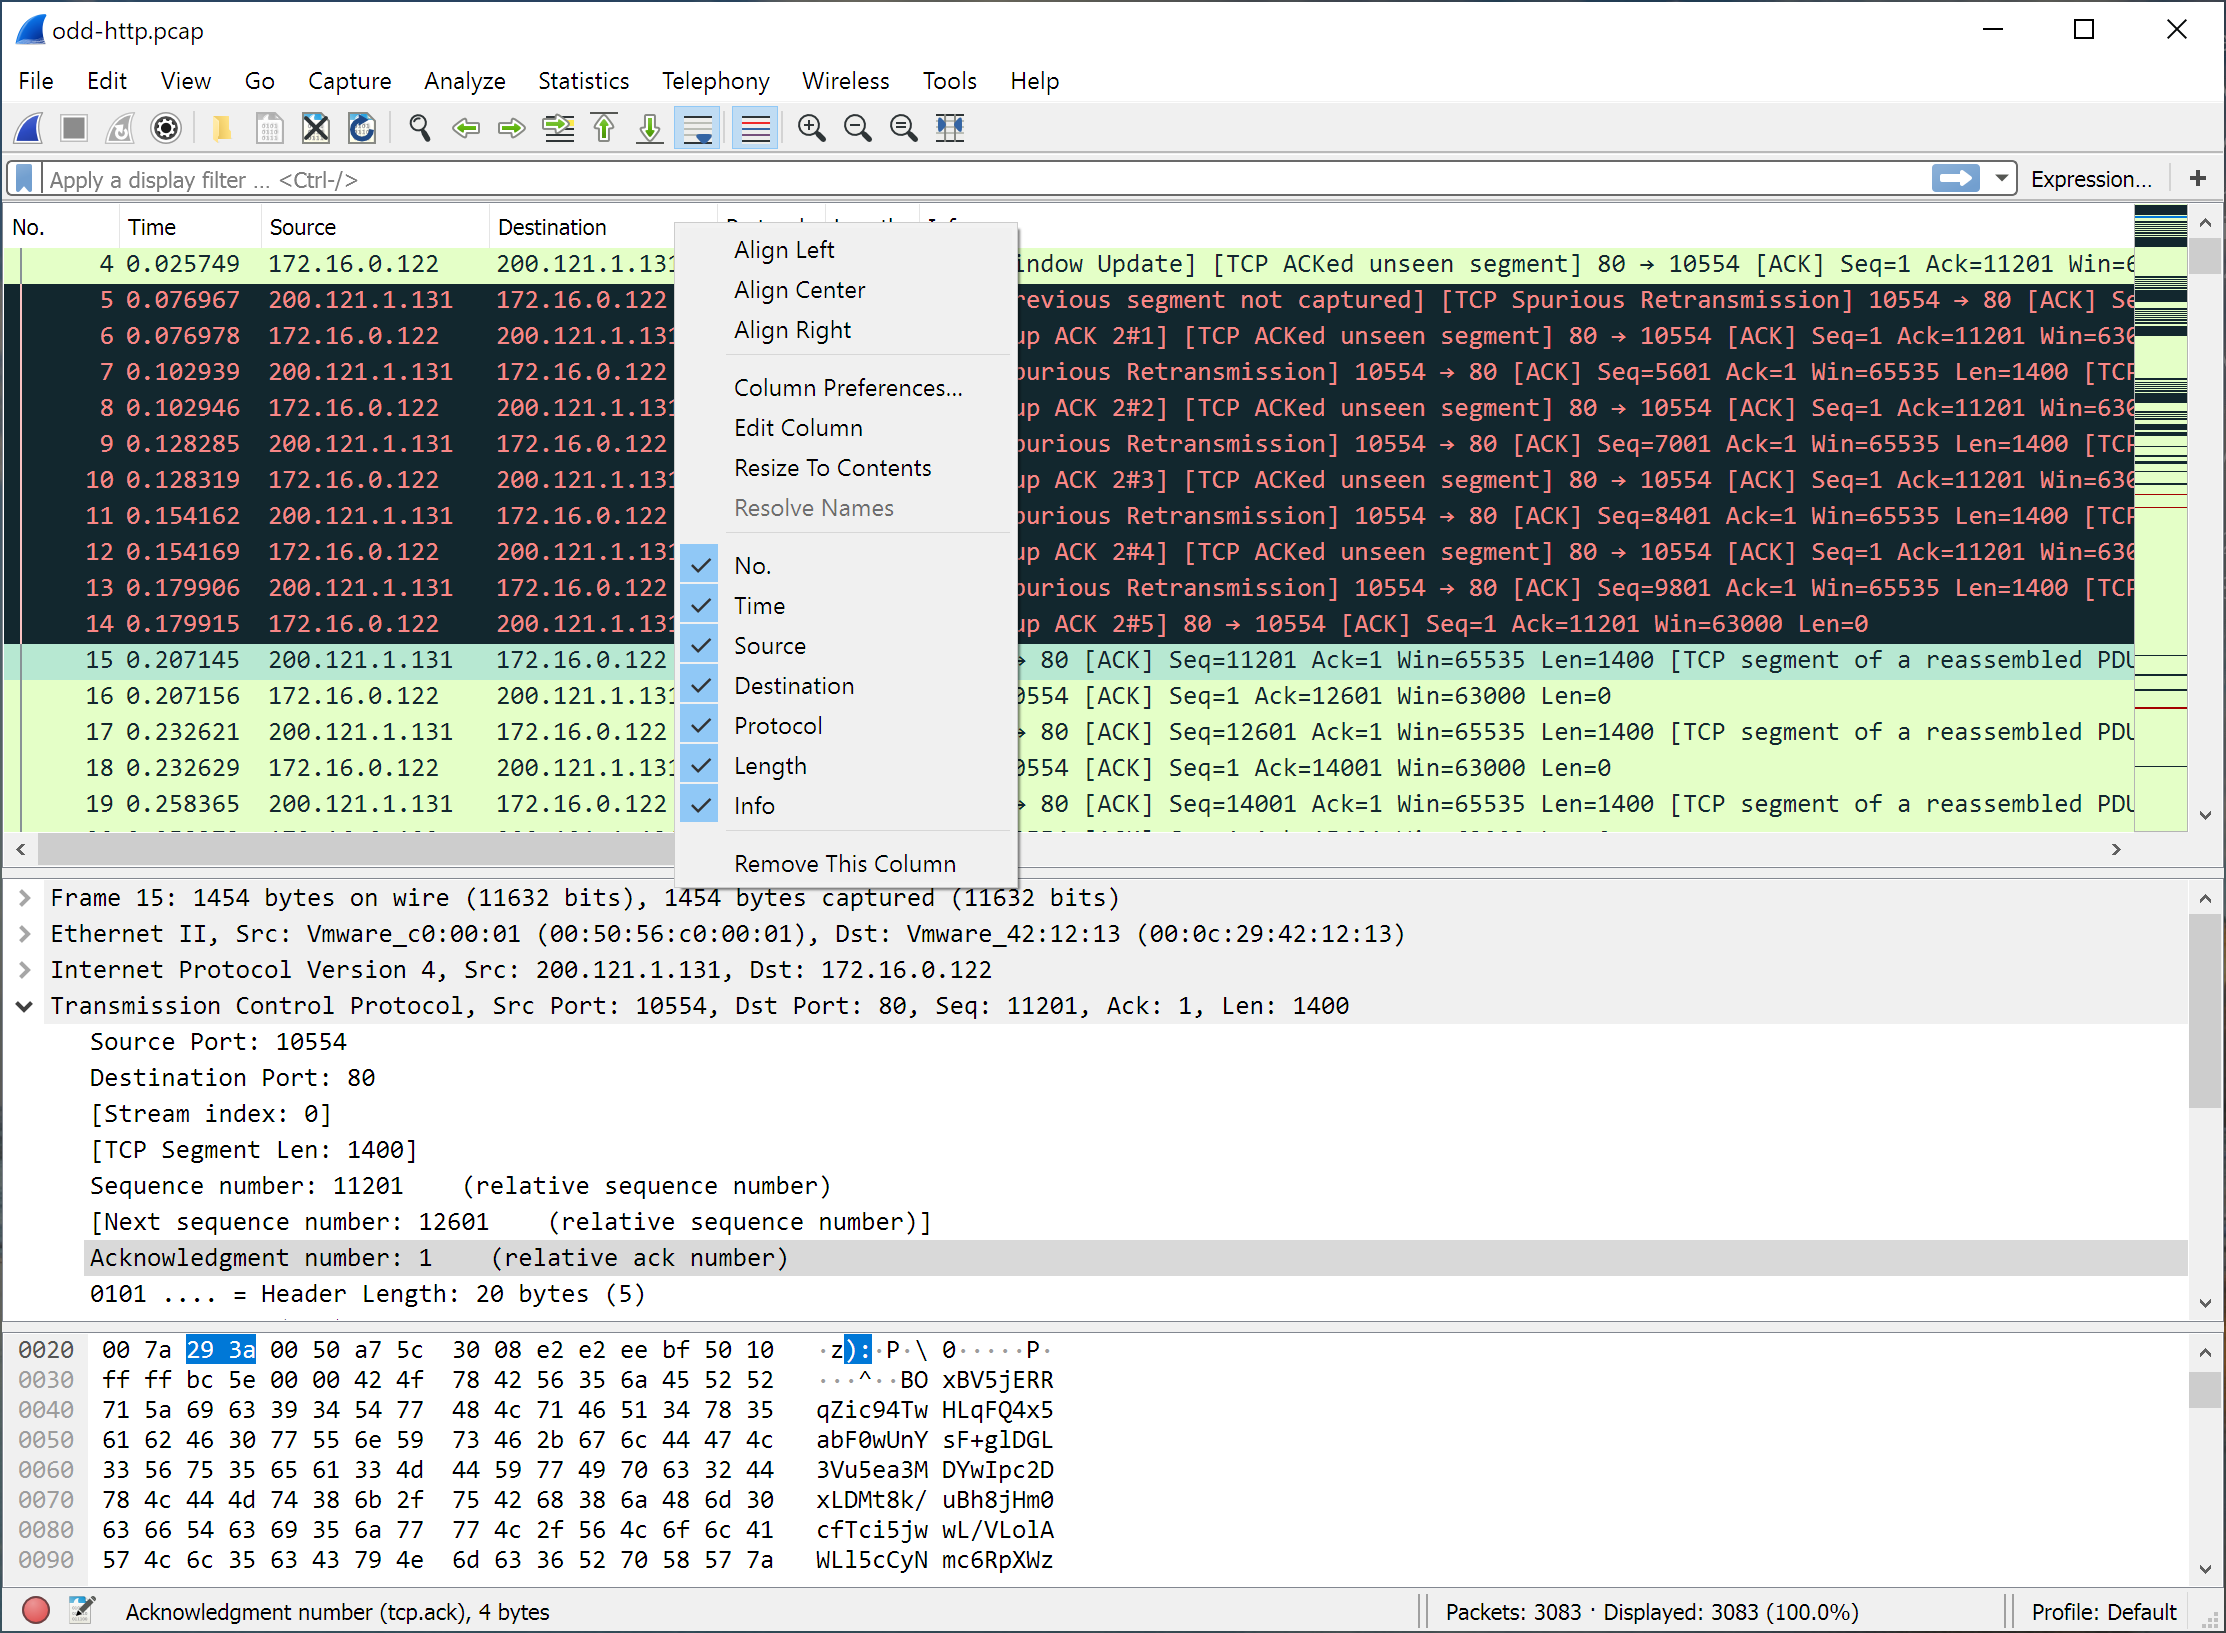
- Standard three-pane packet browser
- Multi-platform: Runs on Windows, Linux, macOS, Solaris, FreeBSD, NetBSD, and many others
- Captured network data can be browsed via a GUI, or via the TTY-mode TShark utility
- The most powerful display filters in the industry
- Rich VoIP analysis
- Read/write many different capture file formats: tcpdump (libpcap), Pcap NG, Catapult DCT2000, Cisco Secure IDS iplog, Microsoft Network Monitor, Network General Sniffer (compressed and uncompressed), Sniffer Pro, and NetXray, Network Instruments Observer, NetScreen snoop, Novell LANalyzer, RADCOM WAN/LAN Analyzer, Shomiti/Finisar Surveyor, Tektronix K12xx, Visual Networks Visual UpTime, WildPackets EtherPeek/TokenPeek/AiroPeek, and many others
- Capture files compressed with gzip can be decompressed on the fly
- Live data can be read from Ethernet, IEEE 802.11, PPP/HDLC, ATM, Bluetooth, USB, Token Ring, Frame Relay, FDDI, and others (depending on your platform)
- Decryption support for many protocols, including IPsec, ISAKMP, Kerberos, SNMPv3, SSL/TLS, WEP, and WPA/WPA2
- Coloring rules can be applied to the packet list for quick, intuitive analysis
- Output can be exported to XML, PostScript®, CSV, or plain text
What's New
The following vulnerabilities have been fixed:
- wnpa-sec-2026-92 ZigBee ZCL protocol dissector crash. CVE-2026-95391.
- wnpa-sec-2026-93 SCTP protocol dissector crash. Issue 21481. CVE-2026-95389.
- wnpa-sec-2026-94 TTL file parser infinite loop. Issue 21501. CVE-2026-95386.
- wnpa-sec-2026-95 PEAK CAN TRC file parser crash. Issue 21503. CVE-2026-95390.
- wnpa-sec-2026-96 IEEE C37.118 Synchrophasor protocol dissector memory leak. Issue 21492. CVE-2026-95395.
- wnpa-sec-2026-97 SPDY protocol dissector crash. Issue 21487. CVE-2026-95387.
- wnpa-sec-2026-98 Microsoft Network Monitor file parser large loop. Issue 21523. CVE-2026-95394.
- wnpa-sec-2026-99 CSN.1 protocol dissector crash. Issue 21510. CVE-2026-95393.
- wnpa-sec-2026-100 MBIM protocol dissector crash. wsbuglink:21549, Issue 21550. CVE-2026-95392.
- wnpa-sec-2026-101 Sharkd utility crash. Issue 21545. CVE-2026-95388.
- wnpa-sec-2026-102 Frame protocol metadissector crash. Issue 21525. CVE-2026-96422.
- wnpa-sec-2026-103 USB HID protocol dissector infinite loop and memory leak. Issue 21566. CVE-2026-96421.
- wnpa-sec-2026-104 RF4CE protocol dissector crash. Issue 21574. CVE-2026-96417.
- wnpa-sec-2026-105 Toshiba file parser crash. Issue 21541. CVE-2026-96420.
- wnpa-sec-2026-106 Profile import crash and possible code execution. Issue 21553. CVE-2026-96419.
- wnpa-sec-2026-107 TIFF protocol dissector infinite loop. Issue 21565. CVE-2026-96418.
- wnpa-sec-2026-108 X11 protocol dissector crash. Issue 21563. CVE-2026-96423.
- wnpa-sec-2026-109 IEEE 802.11 protocol dissector crash. Issue 21564. CVE-2026-96416.
- wnpa-sec-2026-110 Catapult DCT2000 protocol dissector crash. Issue 21589. CVE-2026-96415.
The following bugs have been fixed:
- DICOM Export Objects uint32 length wrap causes undersized allocation and heap overwrite. Issue 21497.
- DICOM AT value formatting has quadratic packet-scope memory amplification. Issue 21498.
- F1AP: NotificationInformation IE under PWSSystemInformation.iE-Extensions not decoded in WriteReplaceWarningRequest. Issue 21499.
- ZDI-CAN-32846: Wireshark LBMC Fragment Reassembly Integer Overflow Remote Code Execution Vulnerability. Issue 21519.
- ZDI-CAN-32851: Wireshark LoRaWAN Decryption Numeric Truncation Error Remote Code Execution Vulnerability. Issue 21520.
- RTPS: dissect_RTPS_DATA_BATCH() sample-info minimum-length check increments the wrong variable (min_len instead of min_length) Issue 21521.
- NULL-pointer dereference in pkcs12 PBE_decrypt_data via empty AlgorithmIdentifier. Issue 21535.
- AKP EncryptedData footer can use an uninitialized tvbuff pointer after malformed OCTET STRING parsing. Issue 21539.
- Out-of-bounds read in DFVM binary-operation error path. Issue 21540.
- Wireshark is not ignoring GREASE values in the JA4 calculation. Issue 21548.
- Bluetooth AVCTP multipart reassembly integer overflow (incomplete AVRCP ckd_add sibling fix) Issue 21552.
- Fuzz job UTF-8 encoding issue: fuzz-2026-09-06-16330342486.pcap. Issue 21562.
- ZDI-CAN-31676: Wireshark SMB Object Export Integer Overflow. Issue 21575.
- Heap out-of-bounds read in FP Hint E-DCH DDI count handling. Issue 21580.
- F1AP fails to decode RRC release message. Issue 21581.
- Stack-based buffer overflow in etwdump extcap (etw_ndiscap.c) when parsing crafted ETL files. Issue 21587.