Google Chrome is a fast, simple, and secure web browser, built for the modern web. Chrome combines a minimal design with sophisticated technology to make the web faster, safer, and easier.
Used by over 3 billion people worldwide, Chrome owes its dominance to a combination of speed, a vast extension ecosystem, and tight integration with Google services.
Is Chrome the fastest browser?
Chrome, Firefox, Safari, and other major browsers are updated every few weeks, making direct speed comparisons a moving target. Chrome has long had a reputation as a RAM hog, but competing browsers can be just as resource-hungry under heavy use.
In recent years Google has added built-in tools to address this. Memory Saver (Settings > Performance) suspends inactive tabs to free up RAM. Google claims up to 40% less memory usage, while Energy Saver reduces background activity when your battery is running low. Both are enabled by default.
Overall, Chrome remains among the fastest browsers for complex web apps and JavaScript-heavy sites. Web developers optimize for Chrome's engine because it is the most-used browser by a wide margin, roughly 68% of global browser share across desktop, Android, and the many other browsers built on the same Chromium engine.
Is Google Chrome safe and private?
Chrome is generally considered safe against malicious websites, phishing, and malware, thanks to features like sandboxing, safe browsing, and AI-powered scam detection. Privacy is a different story.
Everything you do in Chrome (including every character typed into the address bar) is recorded by Google and can be linked to your account and cross-referenced with other Google services. Chrome's Incognito mode does block third-party cookies by default, but it does not prevent Google from seeing your activity. More privacy-conscious users may prefer Firefox, which blocks cross-site tracking by default.
What information does Chrome Sync save?
When signed in, Chrome can save bookmarks, passwords, browsing history, open tabs, settings, themes, extensions, addresses, and other selected data to a Google Account. This information can then be accessed on other devices using the same account. Users can choose which categories are saved instead of synchronizing everything.
To enable it on desktop, click the profile icon in the top-right corner and select Turn On sync. On Android, go to Settings > Account > Sync. On iOS, signing into your Google account in Chrome enables sync automatically. Keep in mind that syncing your data ties it to your Google account, which factors into the privacy trade-offs discussed before.
Does Incognito mode make browsing completely private?
No. Incognito mode prevents Chrome from keeping local browsing history, cookies, and site data after all Incognito windows are closed. However, websites, internet providers, employers, schools, and network administrators may still be able to see browsing activity. Downloads and bookmarks created during the session also remain on the device.
Why is Chrome using so much CPU and memory, even with only a few tabs open?
Chrome's resource appetite is a known issue, but most cases come down to a handful of causes: extension bloat, background processes, and accumulated cache and cookies. Extensions are a particularly common culprit – even idle ones can consume hundreds of megabytes of RAM.
The fastest way to diagnose the problem is Chrome's built-in Task Manager (Shift+Esc, or More Tools > Task Manager), which shows per-tab and per-extension memory and CPU usage. From there you can identify and close the worst offenders. Regularly clearing your browsing data (cache and cookies) can also help over time.
What are the best Chrome alternatives?
There are plenty of free alternatives. For more private browsing, Firefox blocks cross-site tracking by default. If you want a Chrome-like experience without Google's data collection, Ungoogled Chromium removes those integrations entirely.
Microsoft Edge, and Vivaldi are feature-rich Chromium-based options. Edge in particular has grown in popularity and competes seriously on Windows. A new wave of AI browsers has also emerged: Comet and Opera both offer agentic assistants that can summarize content and automate multi-step tasks on your behalf.
Does Chrome update automatically, and how do I check my version?
Yes, Chrome updates silently in the background, so most users never need to think about it. When an update is ready, it downloads automatically and gets applied the next time you relaunch the browser. To check your current version, go to Menu > Help > About Google Chrome. Chrome will check for updates on the spot and prompt you to relaunch if one is pending. Google ships a new major version roughly every four weeks, with security patches in between, so staying current is important.
How can I prevent Chrome from automatically translating web pages?
Chrome's automatic translation feature can be frustrating. To stop this behavior, go to the Settings menu, select "Languages," and turn off the option that offers to translate pages not in a language you read. You can also manage individual language preferences there.
How do I stop websites from sending notifications in Chrome?
Open Settings > Privacy and security > Site settings > Notifications to review which websites are allowed to send alerts. Individual sites can be blocked or removed from the allowed list, and notification requests can be disabled entirely. Similar controls are available for pop-ups, redirects, camera access, and location permissions.
Features

Speed
Chrome is designed to be fast in every possible way: It's quick to start up from your desktop, loads web pages in a snap, and runs complex web applications fast. Learn more about Chrome and speed.
Stay organized with tabs
Tabs help you stay organized, keep track of multiple pages, and multi-task. You can group tabs together for better organization or pin tabs to automatically open websites you use the most.
Have Chrome read pages aloud
Chrome can now read web pages aloud. Words on the page are highlighted to help you follow along. Read aloud is best for content like news stories, articles, or even PDFs.
- To use read aloud, right-click on a page, and select Open in reading mode. This opens the side panel, which has controls you can use for read aloud.
- Click the Play button.
- You can adjust the voice , speed, and highlight style in the toolbar next to the Play button.
View two pages in one tab
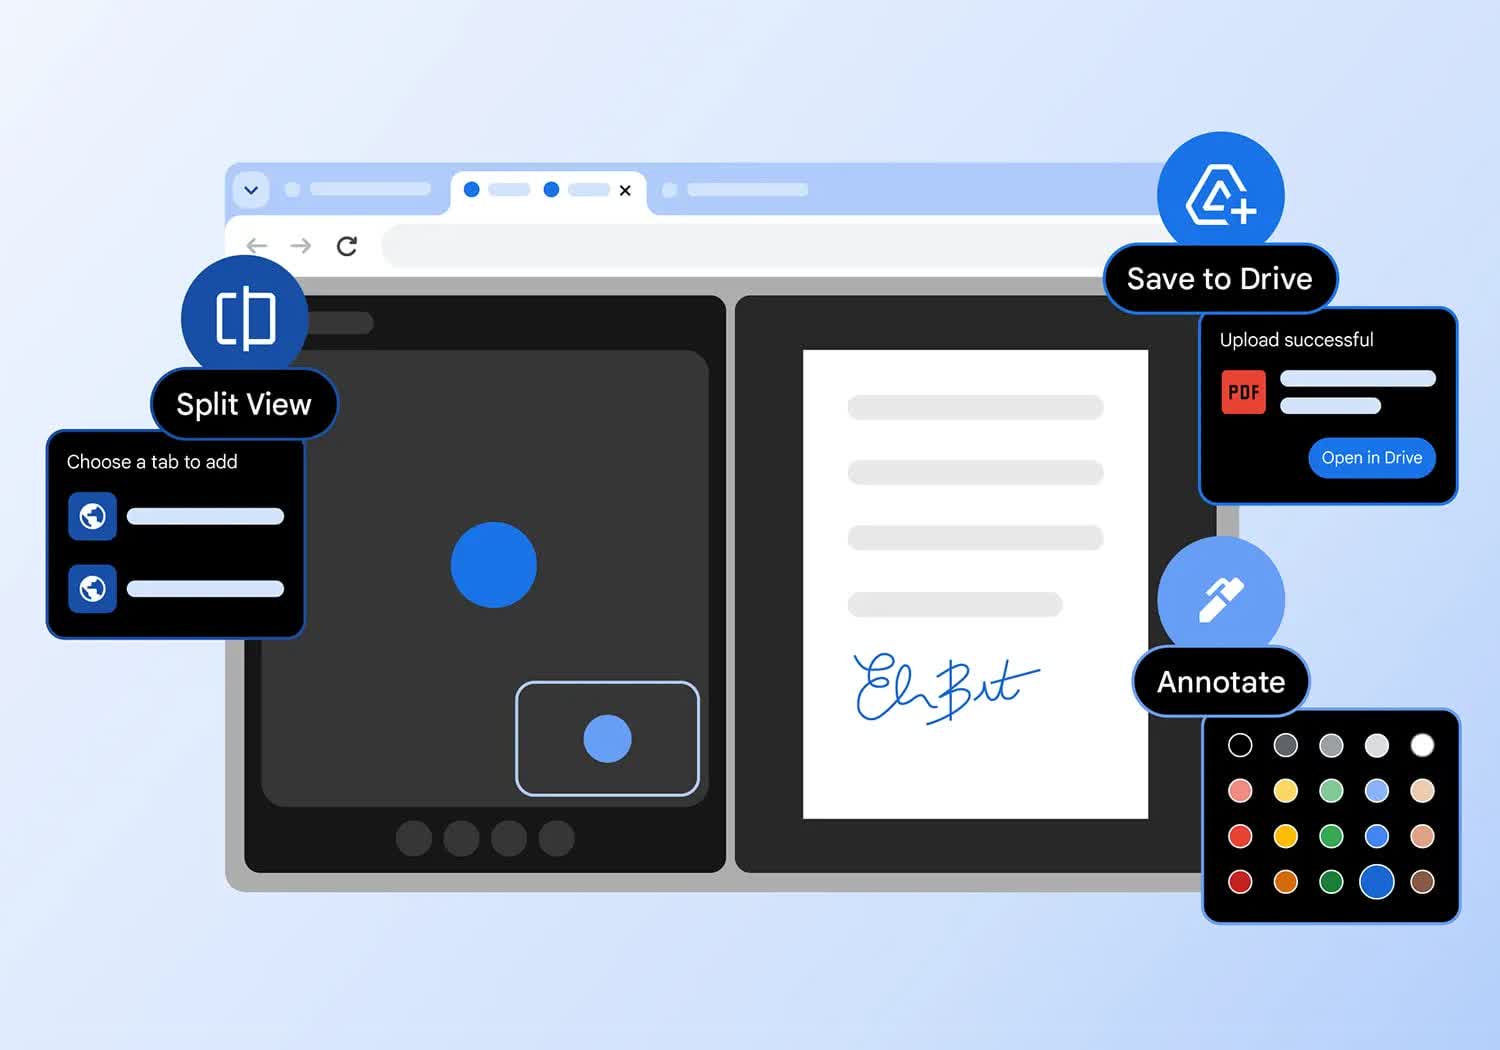
Split view puts two pages side-by-side in the same tab so you can easily compare options, watch a video while taking notes, and more.
Ways to open a split view:
- Drag another tab or link to the left or right edge of your browser window.
- You can also right-click a link and select Open link in split view.
Sign and annotate your PDFs
Skip downloading and printing when it's time to sign a PDF. Use the annotation tool to hand-draw your personal signature, complete forms, and highlight lines.
- Open a PDF and click Annotations.
- Choose your pen or highlighter style and color.
- Draw your annotation or signature, and click Save .
Tip: To make it easier to draw on a small line, Zoom the PDF.
Get your tab groups on the go
Just like your bookmarks and passwords, your tab groups are now available across all your devices. Get started on one device and pick up your project on another device.
To start seeing your tab groups across devices:
- Sign in and create a tab group on your computer or phone.
- Your tab group will automatically save to your account.
- Open your group on a different device.
- Mobile: go to your open tabs, click the tab group section .
- Desktop: click the tab group icon in your bookmarks bar (if open) or the Chrome menu.
What's New
The Chrome team is delighted to announce the promotion of Chrome 153 to the stable channel for Windows, Mac and Linux. This will roll out over the coming days/weeks.
Chrome 153.0.8010.36 (Linux) 153.0.8010.36/.37 Windows/Mac contains a number of fixes and improvements – a list of changes is available in the log. Watch out for upcoming Chrome and Chromium blog posts about new features and big efforts delivered in 153.
Security Fixes and Rewards
Note: Access to bug details and links may be kept restricted until a majority of users are updated with a fix. We will also retain restrictions if the bug exists in a third party library that other projects similarly depend on, but haven't yet fixed.
This update includes 230 security fixes. Please see the Chrome Security Page for more information.
- [$2,500][544163112] Critical CVE-2026-87464: Use after free in WebGL. Reported by Lexi Groves (49016) on 2026-08-08
- [N/A][546252753] Critical CVE-2026-87488: Use after free in WebGL. Reported by Google on 2026-08-14
- [N/A][548127218] Critical CVE-2026-87438: Out of bounds write in WebGL. Reported by Google on 2026-08-18
- [N/A][548130125] Critical CVE-2026-87527: Buffer overflow in WebGL. Reported by Google on 2026-08-18
- [TBD][553770012] Critical CVE-2026-87628: Use after free in Cast. Reported by Hafiizh on 2026-08-28
- [$2,500][541715128] High CVE-2026-87512: Use after free in ANGLE. Reported by weihengqiuu on 2026-08-02
- [$500][540817065] High CVE-2026-87585: Double free in PDFium. Reported by Jeongkihyun on 2026-07-30
- [TBD][489489002] High CVE-2026-87444: Memory corruption in Codecs. Reported by Casper Woudenberg on 2026-03-03
- [N/A][503464711] High CVE-2026-87447: Incorrect authorization in Network. Reported by Google on 2026-04-16
- [N/A][513458719] High CVE-2026-87440: Out of bounds read in Media. Reported by Google on 2026-05-15 [N/A][516996291] High CVE-2026-87633: Use after free in Views. Reported by Google on 2026-05-27
- [N/A][517336350] High CVE-2026-87525: Out of bounds read in Chromoting. Reported by Google on 2026-05-28
- [N/A][517371367] High CVE-2026-87578: Use after free in Receiver. Reported by Google on 2026-05-28
- [N/A][517581661] High CVE-2026-87517: Race condition in Mobile. Reported by Google on 2026-05-28
- [N/A][522546457] High CVE-2026-87524: Use after free in Core. Reported by Google on 2026-06-11
- [N/A][523277481] High CVE-2026-87569: Missing authorization in Views. Reported by Google on 2026-06-12
- [N/A][524423633] High CVE-2026-87554: Race condition in Chromoting. Reported by Google on 2026-06-16
- [N/A][524453236] High CVE-2026-87467: Race condition in Updater. Reported by Google on 2026-06-16
- [TBD][529123409] High CVE-2026-87492: Incorrect authorization in DevTools. Reported by Avadhut Mahamuni on 2026-06-29
- [N/A][529878021] High CVE-2026-87520: Use after free in Dawn. Reported by Google on 2026-06-30
- [N/A][532916987] High CVE-2026-87514: Use after free in Views. Reported by Google on 2026-07-09
- [N/A][534912743] High CVE-2026-87650: Out of bounds read in WebGL. Reported by Google on 2026-07-14
- [N/A][536434693] High CVE-2026-87596: Out of bounds read in ANGLE. Reported by Google on 2026-07-19
- [N/A][536444790] High CVE-2026-87654: Buffer overflow in ANGLE. Reported by Google on 2026-07-19
- [N/A][536648007] High CVE-2026-87604: Out of bounds read in ANGLE. Reported by Google on 2026-07-19
- [N/A][536664909] High CVE-2026-87621: Out of bounds write in ANGLE. Reported by Google on 2026-07-20
- [N/A][536673946] High CVE-2026-87647: Uninitialized resource in GPU. Reported by Google on 2026-07-20
- [TBD][539754136] High CVE-2026-87646: Use after free in Web Authentication. Reported by h3ee on 2026-07-28
- [N/A][540019091] High CVE-2026-87500: Improper validation of array index in ANGLE. Reported by Google on 2026-07-28
- [N/A][540021969] High CVE-2026-87572: Injection in DevTools. Reported by Google on 2026-07-28
- [N/A][540058837] High CVE-2026-87460: Use after free in Platform. Reported by Google on 2026-07-28
- [N/A][542756749] High CVE-2026-87542: Use after free in Input. Reported by Google BigSleep@Grape on 2026-08-05
- [TBD][544415098] High CVE-2026-87639: Use after free in WebPackaging. Reported by OpenAI Codex Security (amyb) on 2026-08-09
- [TBD][547426657] High CVE-2026-87552: Missing authorization in TrustedWebActivities. Reported by juddrouillon0 on 2026-08-16
- [TBD][550141694] High CVE-2026-87651: Incorrect authorization in Paint. Reported by OGINOME Tomohito on 2026-08-21
- [TBD][550360762] High CVE-2026-87587: Use after free in V8. Reported by Jihyeon Jeong (Compsec Lab, Seoul National University / Research Intern) on 2026-08-21
- [TBD][552342545] High CVE-2026-87564: Type confusion in V8. Reported by Tech Division (@taiphung) - Mobifone Digital Payment on 2026-08-25
- [N/A][552413517] High CVE-2026-87498: Missing authorization in WebUI. Reported by Google on 2026-08-25
- [N/A][553118043] High CVE-2026-87499: Incorrect authorization in Network. Reported by Google on 2026-08-26
- [N/A][553122131] High CVE-2026-87607: Use after free in Device. Reported by Google on 2026-08-26
- [N/A][553128689] High CVE-2026-87558: Use after free in Payments. Reported by Google on 2026-08-26
- [N/A][553129531] High CVE-2026-87581: Use after free in Payments. Reported by Google on 2026-08-26
- [N/A][553928324] High CVE-2026-87480: Use after free in Printing. Reported by Google on 2026-08-28
- [TBD][554236352] High CVE-2026-87612: Type confusion in V8. Reported by ywatanabee on 2026-08-29
- [TBD][554421904] High CVE-2026-87536: Use after free in V8. Reported by StinkyTuna56 on 2026-08-29
- [N/A][554558968] High CVE-2026-87474: Use after free in Payments. Reported by Google on 2026-08-29
- [$5,000][499206649] Medium CVE-2026-87504: Use after free in Core. Reported by c6eed09fc8b174b0f3eebedcceb1e792 on 2026-04-03
- [$3,000][498482618] Medium CVE-2026-87640: Out of bounds read in WebView. Reported by c6eed09fc8b174b0f3eebedcceb1e792 on 2026-04-01
- [$2,500][543557673] Medium CVE-2026-87491: Out of bounds write in V8. Reported by Jihyeon Jeong (Compsec Lab, Seoul National University / Research Intern) on 2026-08-06
- [$2,000][40060525] Medium CVE-2026-87478: Observable discrepancy in Autofill. Reported by Maurice Dauer on 2022-08-07
- [$2,000][483435192] Medium CVE-2026-87446: Incomplete cleanup in Extensions. Reported by Hafiizh on 2026-02-11
- [$1,000][542146471] Medium CVE-2026-87657: Use after free in V8. Reported by Jihyeon Jeong (Compsec Lab, Seoul National University / Research Intern) on 2026-08-03
- [N/A][493322521] Medium CVE-2026-87434: Missing authorization in CORS. Reported by Google on 2026-03-17
- [N/A][495429423] Medium CVE-2026-87487: Missing authorization in FileSystem. Reported by Google on 2026-03-23
- [N/A][495444970] Medium CVE-2026-87453: Confused deputy in BackgroundFetch. Reported by Google on 2026-03-23
- [N/A][495515356] Medium CVE-2026-87588: Use after free in Chromecast. Reported by Google on 2026-03-23
- [N/A][495541478] Medium CVE-2026-87636: Type confusion in XML. Reported by Google on 2026-03-23
- [N/A][495876543] Medium CVE-2026-87611: Missing authorization in FileSystem. Reported by Google on 2026-03-24
- [N/A][495933780] Medium CVE-2026-87606: Missing authorization in SiteIsolation. Reported by Google on 2026-03-25
- [N/A][496231550] Medium CVE-2026-87456: Uninitialized resource in Media. Reported by Google on 2026-03-25
- [N/A][496595299] Medium CVE-2026-87553: Improper input validation in SiteIsolation. Reported by Google on 2026-03-26
- [N/A][496615345] Medium CVE-2026-87658: Information leak in Extensions. Reported by Google on 2026-03-26
- [N/A][496616790] Medium CVE-2026-87465: Incorrect authorization in Downloads. Reported by Google on 2026-03-26
- [N/A][497093426] Medium CVE-2026-87515: Incorrect authorization in FileAPI. Reported by Google on 2026-03-28
- [N/A][497111188] Medium CVE-2026-87547: Incorrect reference resolution in FileSystem. Reported by Google on 2026-03-28
- [N/A][497443419] Medium CVE-2026-87442: Confused deputy in Prerender. Reported by Google on 2026-03-29
- [N/A][497551905] Medium CVE-2026-87506: Privilege elevation in WebUI. Reported by Google on 2026-03-29
- [N/A][497574154] Medium CVE-2026-87433: Race condition in FileAPI. Reported by Google on 2026-03-30
- [N/A][497635917] Medium CVE-2026-87557: Missing authorization in LocalNetworkAccess. Reported by Google on 2026-03-30
- [N/A][497837188] Medium CVE-2026-87457: Race condition in Updater. Reported by Google on 2026-03-30
- [N/A][497986036] Medium CVE-2026-87503: Inappropriate implementation in Downloads. Reported by Google on 2026-03-31
- [N/A][498730641] Medium CVE-2026-87481: Incorrect authorization in WebView. Reported by Google on 2026-04-01
- [N/A][498732709] Medium CVE-2026-87537: Missing authorization in Extensions. Reported by Google on 2026-04-01
- [N/A][498869663] Medium CVE-2026-87471: Incorrect authorization in ServiceWorker. Reported by Google on 2026-04-02
- [N/A][499230506] Medium CVE-2026-87485: Incorrect authorization in CORS. Reported by Google on 2026-04-03
- [N/A][499425100] Medium CVE-2026-87652: Incorrect authorization in PushAPI. Reported by Google on 2026-04-04
- [N/A][500094528] Medium CVE-2026-87582: Confused deputy in DataTransfer. Reported by Google on 2026-04-06
- [N/A][500467033] Medium CVE-2026-87466: Incorrect authorization in Workers. Reported by Google on 2026-04-07
- [N/A][501627201] Medium CVE-2026-87603: Missing authorization in FileSystem. Reported by Google on 2026-04-11
- [N/A][501643868] Medium CVE-2026-87615: Race condition in Payments. Reported by Google on 2026-04-11
- [N/A][501644790] Medium CVE-2026-87642: Uninitialized resource in WebGL. Reported by Google on 2026-04-11
- [N/A][501700023] Medium CVE-2026-87577: Incorrect authorization in Isolated. Reported by Google on 2026-04-11
- [N/A][501850947] Medium CVE-2026-87449: Cross-site request forgery in DeviceBoundSessionCredentials. Reported by Google on 2026-04-12
- [N/A][501889544] Medium CVE-2026-87613: Incorrect reference resolution in Extensions. Reported by Google on 2026-04-12
- [N/A][502611474] Medium CVE-2026-87645: Improper state validation in Safebrowsing. Reported by Google on 2026-04-14
- [N/A][502768228] Medium CVE-2026-87443: Missing authorization in Actor. Reported by Google on 2026-04-15
- [TBD][502783118] Medium CVE-2026-87630: Integer overflow in WebRTC. Reported by ngrunbaum on 2026-04-15
- [N/A][502814490] Medium CVE-2026-87590: Improper input validation in Passwords. Reported by Google on 2026-04-15
- [N/A][502986244] Medium CVE-2026-87580: Incorrect authorization in WebAppInstalls. Reported by Google on 2026-04-15
- [N/A][503736006] Medium CVE-2026-87482: Cleartext transmission of sensitive data in HttpsUpgrades. Reported by Google on 2026-04-17
- [N/A][504670493] Medium CVE-2026-87497: Uninitialized resource in Codecs. Reported by Google on 2026-04-20
- [N/A][504690157] Medium CVE-2026-87579: Buffer overflow in WebRTC. Reported by Google on 2026-04-20
- [N/A][506385755] Medium CVE-2026-87576: Uninitialized resource in GPU. Reported by Google on 2026-04-25
- [N/A][506390077] Medium CVE-2026-87476: Incorrect authorization in Loader. Reported by Google on 2026-04-25
- [N/A][507225626] Medium CVE-2026-87475: Missing authorization in Omnibox. Reported by Google on 2026-04-28
- [N/A][511754574] Medium CVE-2026-87436: Incomplete cleanup in Browser. Reported by Google on 2026-05-10
- [N/A][511772271] Medium CVE-2026-87479: Insufficient policy enforcement in Extensions. Reported by Google on 2026-05-10
- [N/A][511773417] Medium CVE-2026-87513: Missing authorization in ControlledFrame. Reported by Google on 2026-05-10
- [N/A][511820041] Medium CVE-2026-87432: Incorrect authorization in Navigation. Reported by Google on 2026-05-10
- [N/A][511824746] Medium CVE-2026-87560: Missing authorization in Browser. Reported by Google on 2026-05-10
- [N/A][512986143] Medium CVE-2026-87521: Information leak in WebMCP. Reported by Google on 2026-05-13
- [N/A][513003268] Medium CVE-2026-87539: Observable discrepancy in Network. Reported by Google on 2026-05-14
- [N/A][513048243] Medium CVE-2026-87648: Use after free in ANGLE. Reported by Google on 2026-05-14
- [N/A][513134173] Medium CVE-2026-87534: Missing authorization in WebView. Reported by Google on 2026-05-14
- [N/A][513135531] Medium CVE-2026-87562: Incorrect reference resolution in Accessibility. Reported by Google on 2026-05-14
- [N/A][513192482] Medium CVE-2026-87556: Missing authorization in Browser. Reported by Google on 2026-05-14
- [N/A][513346220] Medium CVE-2026-87508: Incorrect authorization in Loader. Reported by Google on 2026-05-14
- [N/A][513416699] Medium CVE-2026-87643: Integer overflow in GPU. Reported by Google on 2026-05-15
- [N/A][513438970] Medium CVE-2026-87573: Improper input validation in Network. Reported by Google on 2026-05-15
- [N/A][513495219] Medium CVE-2026-87548: Improper state validation in Installer. Reported by Google on 2026-05-15
- [N/A][513509804] Medium CVE-2026-87501: UI misrepresentation in Passwords. Reported by Google on 2026-05-15
- [N/A][513524705] Medium CVE-2026-87452: Incorrect authorization in GPU. Reported by Google on 2026-05-15
- [N/A][513608513] Medium CVE-2026-87516: Observable discrepancy in Navigation. Reported by Google on 2026-05-15
- [N/A][513702096] Medium CVE-2026-87599: Improper input validation in Interstitials. Reported by Google on 2026-05-16
- [N/A][514009699] Medium CVE-2026-87507: UI misrepresentation in Downloads. Reported by Google on 2026-05-17
- [N/A][514011926] Medium CVE-2026-87559: UI misrepresentation in UI. Reported by Google on 2026-05-17
- [N/A][514016678] Medium CVE-2026-87472: Improper input validation in FedCM. Reported by Google on 2026-05-17
- [N/A][514017067] Medium CVE-2026-87486: Clickjacking in TrustedWebActivities. Reported by Google on 2026-05-17
- [N/A][514023309] Medium CVE-2026-87655: Clickjacking in Downloads. Reported by Google on 2026-05-17
- [N/A][514041087] Medium CVE-2026-87462: UI misrepresentation in FedCM. Reported by Google on 2026-05-17
- [N/A][514055890] Medium CVE-2026-87649: UI misrepresentation in Downloads. Reported by Google on 2026-05-17
- [N/A][514056835] Medium CVE-2026-87445: UI misrepresentation in Session. Reported by Google on 2026-05-17
- [N/A][514069596] Medium CVE-2026-87567: UI misrepresentation in UrlFormatting. Reported by Google on 2026-05-17
- [N/A][514074827] Medium CVE-2026-87496: UI misrepresentation in Browser. Reported by Google on 2026-05-17
- [N/A][514556469] Medium CVE-2026-87441: Missing authorization in Downloads. Reported by Google on 2026-05-19
- [N/A][516534546] Medium CVE-2026-87549: Incomplete cleanup in Downloads. Reported by Google on 2026-05-25
- [N/A][517072005] Medium CVE-2026-87458: UI misrepresentation in Geometry. Reported by Google on 2026-05-27
- [N/A][517092658] Medium CVE-2026-87574: Information leak in ServiceWorker. Reported by Google on 2026-05-27
- [N/A][517122234] Medium CVE-2026-87495: Information leak in Scroll. Reported by Google on 2026-05-27
- [N/A][517156678] Medium CVE-2026-87541: Information leak in Navigation. Reported by Google on 2026-05-27
- [N/A][517178299] Medium CVE-2026-87451: Information leak in Downloads. Reported by Google on 2026-05-27
- [N/A][517215407] Medium CVE-2026-87570: Incorrect authorization in SiteIsolation. Reported by Google on 2026-05-27
- [N/A][517337579] Medium CVE-2026-87555: Uninitialized resource in GPU. Reported by Google on 2026-05-28
- [N/A][517339356] Medium CVE-2026-87600: Improper input validation in Safebrowsing. Reported by Google on 2026-05-28
- [N/A][517369256] Medium CVE-2026-87532: Improper state validation in Safebrowsing. Reported by Google on 2026-05-28
- [N/A][517415433] Medium CVE-2026-87439: Information leak in ServiceWorker. Reported by Google on 2026-05-28
- [N/A][517432155] Medium CVE-2026-87450: Incorrect authorization in Permissions. Reported by Google on 2026-05-28
- [N/A][517597701] Medium CVE-2026-87505: Incorrect authorization in FileSystem. Reported by Google on 2026-05-28
- [N/A][517602176] Medium CVE-2026-87622: Missing authorization in FedCM. Reported by Google on 2026-05-28
- [N/A][517721914] Medium CVE-2026-87540: Incorrect authorization in Isolated. Reported by Google on 2026-05-29
- [N/A][517732336] Medium CVE-2026-87594: Incorrect authorization in DataTransfer. Reported by Google on 2026-05-29
- [N/A][517917560] Medium CVE-2026-87518: Observable discrepancy in Safebrowsing. Reported by Google on 2026-05-29
- [N/A][518002426] Medium CVE-2026-87589: Incorrect authorization in SiteIsolation. Reported by Google on 2026-05-29
- [N/A][518039263] Medium CVE-2026-87484: UI misrepresentation in Geometry. Reported by Google on 2026-05-29
- [N/A][518081914] Medium CVE-2026-87530: Uncontrolled search path element in CredentialProvider. Reported by Google on 2026-05-30
- [N/A][518082852] Medium CVE-2026-87550: Improper encoding or escaping of output in CSS. Reported by Google on 2026-05-30
- [N/A][520161438] Medium CVE-2026-87494: Use after free in Browser. Reported by Google on 2026-06-05
- [N/A][520201931] Medium CVE-2026-87483: Incorrect authorization in Browser. Reported by Google on 2026-06-05
- [N/A][520389619] Medium CVE-2026-87454: Information leak in Enterprise. Reported by Google on 2026-06-05
- [N/A][520469117] Medium CVE-2026-87616: Improper initialization in Views. Reported by Google on 2026-06-05
- [N/A][520572550] Medium CVE-2026-87535: Information loss or omission in Safebrowsing. Reported by Google on 2026-06-06
- [N/A][521616899] Medium CVE-2026-87644: Incorrect authorization in Views. Reported by Google on 2026-06-09
- [N/A][521620916] Medium CVE-2026-87533: Use after free in DevTools. Reported by Google on 2026-06-09
- [N/A][522304737] Medium CVE-2026-87635: UI misrepresentation in Payments. Reported by Google on 2026-06-10
- [N/A][523091391] Medium CVE-2026-87641: Race condition in Browser. Reported by Google on 2026-06-12
- [N/A][523313374] Medium CVE-2026-87431: Missing authorization in Extensions. Reported by Microsoft Edge on 2026-06-12
- [N/A][523741272] Medium CVE-2026-87493: Missing authorization in FileSystem. Reported by Google on 2026-06-14
- [N/A][532921336] Medium CVE-2026-87625: Use after free in V8. Reported by Google on 2026-07-09
- [N/A][532931962] Medium CVE-2026-87468: Incorrect authorization in Isolated. Reported by Google on 2026-07-09
- [N/A][532952073] Medium CVE-2026-87563: Origin validation error in Paint. Reported by Google on 2026-07-09
- [N/A][532957878] Medium CVE-2026-87510: Improper input validation in FileAPI. Reported by Google on 2026-07-09
- [N/A][533070113] Medium CVE-2026-87435: Information leak in ControlledFrame. Reported by Google on 2026-07-09
- [N/A][533597592] Medium CVE-2026-87531: Information leak in CORS. Reported by Google on 2026-07-11
- [N/A][534863145] Medium CVE-2026-87637: Use after free in Extensions. Reported by Google on 2026-07-14
- [N/A][536423794] Medium CVE-2026-87529: Numeric truncation error in Media. Reported by Google on 2026-07-19
- [N/A][536446354] Medium CVE-2026-87470: Improper quantity validation in Tint. Reported by Google on 2026-07-19
- [N/A][536598187] Medium CVE-2026-87586: Out of bounds read in ANGLE. Reported by Google on 2026-07-19
- [N/A][537466493] Medium CVE-2026-87584: Incorrect authorization in WebUI. Reported by Google on 2026-07-21
- [TBD][538197156] Medium CVE-2026-87632: Cross-site scripting in SanitizerAPI. Reported by Eli Ainhorn on 2026-07-24
- [N/A][539569491] Medium CVE-2026-87528: Type confusion in Rust. Reported by marcobartoli on 2026-07-27
- [N/A][540015493] Medium CVE-2026-87623: Observable discrepancy in DOM. Reported by Google on 2026-07-28
- [N/A][540021850] Medium CVE-2026-87566: Observable discrepancy in Layout. Reported by Google on 2026-07-28
- [N/A][540024134] Medium CVE-2026-87638: Out of bounds write in Media. Reported by Google on 2026-07-28
- [N/A][542565481] Medium CVE-2026-87455: Use after free in Aura. Reported by Microsoft on 2026-08-04
- [TBD][543938457] Medium CVE-2026-87591: Incorrect authorization in Extensions. Reported by antoniosmr02 on 2026-08-07
- [N/A][544484669] Medium CVE-2026-87526: Use after free in Passwords. Reported by shab on 2026-08-10
- [N/A][547322272] Medium CVE-2026-87609: Use after free in Sharing. Reported by Google on 2026-08-16
- [TBD][547592631] Medium CVE-2026-87610: Incorrect authorization in Omnibox. Reported by Arni Hardarson (Neonix Security) on 2026-08-17
- [N/A][553155590] Medium CVE-2026-87626: Incorrect authorization in DeviceBoundSessionCredentials. Reported by Google on 2026-08-26
- [$1,500][490773579] Low CVE-2026-87629: Incorrect authorization in Sources. Reported by lebr0nli of National Yang Ming Chiao Tung University, Dept. of CS, Security and Systems Lab on 2026-03-08
- [$500][40058710] Low CVE-2026-87653: UI misrepresentation in FullScreen. Reported by Lijo A.T on 2022-02-07
- [N/A][349994197] Low CVE-2026-87634: Use after free in WebPackaging. Reported by Google on 2024-06-28
- [N/A][497025031] Low CVE-2026-87429: Missing authorization in ServiceWorker. Reported by Google on 2026-03-27
- [N/A][497203958] Low CVE-2026-87618: Incorrect reference resolution in Storage. Reported by Google on 2026-03-28
- [N/A][497359396] Low CVE-2026-87614: Incorrect authorization in ServiceWorker. Reported by Google on 2026-03-29
- [N/A][497433347] Low CVE-2026-87619: Observable discrepancy in Prefetch. Reported by Google on 2026-03-29
- [N/A][499217288] Low CVE-2026-87561: Incorrect authorization in Web Authentication. Reported by Google on 2026-04-03
- [N/A][499218516] Low CVE-2026-87598: Incorrect authorization in ServiceWorker. Reported by Google on 2026-04-03
- [N/A][501763003] Low CVE-2026-87519: Incorrect authorization in Safebrowsing. Reported by Google on 2026-04-11
- [N/A][502452118] Low CVE-2026-87543: Missing authorization in Core. Reported by Google on 2026-04-14
- [N/A][507219126] Low CVE-2026-87522: Missing authorization in WebView. Reported by Google on 2026-04-28
- [N/A][513143955] Low CVE-2026-87568: Improper input validation in Chromium. Reported by Google on 2026-05-14
- [N/A][513245072] Low CVE-2026-87656: Improper state validation in Safebrowsing. Reported by Google on 2026-05-14
- [N/A][513395384] Low CVE-2026-87511: Missing authorization in DevTools. Reported by Google on 2026-05-15
- [N/A][513473551] Low CVE-2026-87627: Interpretation conflict in Safebrowsing. Reported by Google on 2026-05-15
- [N/A][513726466] Low CVE-2026-87595: Server-side request forgery in Mobile. Reported by Google on 2026-05-16
- [N/A][513947572] Low CVE-2026-87592: Out of bounds read in Tint. Reported by Google on 2026-05-17
- [N/A][514489101] Low CVE-2026-87620: Observable discrepancy in SVG. Reported by Google on 2026-05-19
- [N/A][515426792] Low CVE-2026-87502: Confused deputy in Fullscreen. Reported by Google on 2026-05-21
- [N/A][516965176] Low CVE-2026-87448: Use after free in DevTools. Reported by Google on 2026-05-27
- [N/A][517219513] Low CVE-2026-87459: Observable discrepancy in Select. Reported by Google on 2026-05-27
- [N/A][517776674] Low CVE-2026-87463: Incorrect authorization in Certificate. Reported by Google on 2026-05-29
- [N/A][517926950] Low CVE-2026-87546: Incorrect type conversion or cast in Safebrowsing. Reported by Google on 2026-05-29
- [N/A][522399466] Low CVE-2026-87538: Clickjacking in Input. Reported by Google on 2026-06-10
- [N/A][523243507] Low CVE-2026-87545: Information leak in Mobile. Reported by Google on 2026-06-12
- [N/A][523442920] Low CVE-2026-87617: Use after free in DevTools. Reported by Google on 2026-06-13
- [N/A][532933816] Low CVE-2026-87523: Race condition in DataTransfer. Reported by Google on 2026-07-09
- [N/A][532968511] Low CVE-2026-87565: Information leak in Passwords. Reported by Google on 2026-07-09
- [N/A][533018632] Low CVE-2026-87597: UI misrepresentation in CustomTabs. Reported by Google on 2026-07-09
- [N/A][533044125] Low CVE-2026-87624: UI misrepresentation in Passwords. Reported by Google on 2026-07-09
- [N/A][533084499] Low CVE-2026-87605: Missing authorization in Contacts. Reported by Google on 2026-07-09
- [N/A][533112829] Low CVE-2026-87490: Information leak in Transactions Platform. Reported by Google on 2026-07-09
- [N/A][533116484] Low CVE-2026-87583: UI misrepresentation in Passwords. Reported by Google on 2026-07-09
- [N/A][535718578] Low CVE-2026-87509: Incorrect authorization in Updater. Reported by Google on 2026-07-16
- [N/A][537101736] Low CVE-2026-87473: Incorrect authorization in FileHandling. Reported by Google on 2026-07-21
- [N/A][537470182] Low CVE-2026-87461: Information leak in Core. Reported by Google on 2026-07-21
- [N/A][537476242] Low CVE-2026-87631: Missing authorization in DOM. Reported by Google on 2026-07-21
- [TBD][538715523] Low CVE-2026-87469: Improper input validation in Extensions. Reported by Jeong Woo Lee (@eclipse07077) on 2026-07-24
- [N/A][539453394] Low CVE-2026-87489: Memory corruption in V8. Reported by Google on 2026-07-27
- [N/A][540013886] Low CVE-2026-87575: Incorrect authorization in Loader. Reported by Google on 2026-07-28
- [N/A][540046516] Low CVE-2026-87571: Improper certificate validation in Loader. Reported by Google on 2026-07-28
- [N/A][540059211] Low CVE-2026-87477: Information leak in Core. Reported by Google on 2026-07-28
- [N/A][540070236] Low CVE-2026-87551: Improper certificate validation in CORS. Reported by Google on 2026-07-28
- [N/A][540072282] Low CVE-2026-87608: Improper certificate validation in FedCM. Reported by Google on 2026-07-28
- [N/A][540082621] Low CVE-2026-87437: Information leak in Frames. Reported by Google on 2026-07-28
- [TBD][541546782] Low CVE-2026-87602: Out of bounds read in ANGLE. Reported by Hyeongeun Ji of JeroScope on 2026-08-01
- [TBD][541604100] Low CVE-2026-87601: Race condition in V8. Reported by Salvatore Gulizia (nickname: Serotav) on 2026-08-01
- [TBD][542355360] Low CVE-2026-87544: Incorrect authorization in Extensions. Reported by antoniosmr02 on 2026-08-04
- [TBD][542449805] Low CVE-2026-87430: Buffer overflow in WebRTC. Reported by k-kyuno on 2026-08-04
- [N/A][553252820] Low CVE-2026-87593: Information leak in Editing. Reported by Google on 2026-08-27
Google is aware that an exploit for CVE-2026-87491 exists in the wild.
We would also like to thank all security researchers that worked with us during the development cycle to prevent security bugs from ever reaching the stable channel.
Many of our security bugs are detected using AddressSanitizer, MemorySanitizer, UndefinedBehaviorSanitizer, Control Flow Integrity, libFuzzer, or AFL.
Google Chrome adds split view, PDF annotations, and Drive saves
Google is making Chrome a little more work-friendly with a trio of productivity upgrades that are now rolling out on the desktop. The browser's new built-in split view lets you run two tabs side by side without juggling windows, while its PDF viewer can now handle highlights, notes, and even signatures.
There's also a smarter Save to Google Drive option that sends PDFs straight into a dedicated "Saved from Chrome" folder, cutting out the download-and-reupload dance. If you live in your browser all day, the latest Chrome update is worth grabbing.