A Bluetooth glitch exposed AliExpress's hidden audio fingerprinting
A hot potato: As cookies become a less reliable way to track people online, AliExpress may be showing how far companies will go to fill that gap. Researchers found code on the site's homepage that ran silent audio processes in the browser. Tied to Alibaba's security systems, the scripts tap a device's own audio hardware to generate a signal and measure the tiny, device-specific ways it comes back – producing something close to a fingerprint that doesn't need a single cookie to work. It's the kind of tracking a user would likely never notice.
The WhisperPair vulnerability affects headphones and speakers from major brands
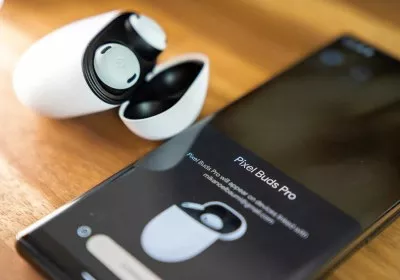
Winners & losers: Google's Fast Pair technology was designed for convenience. The protocol turns pairing a new Bluetooth accessory into a tap-and-go experience for Android and Chrome OS users. But new research suggests that the same design choices that make Fast Pair effortless also make it alarmingly easy to abuse.